Hackers have stopped factories producing cars, prevented hospitals from processing blood tests and forced international airports back towards manual check-in.
What makes us believe banking and payment systems are somehow untouchable?
They are not untouchable. They are simply the systems we cannot afford to lose.
Over recent decades, we have transferred an extraordinary proportion of our lives—and almost all our money—into a digital world.
Our bank balances are numbers on screens. Our investments are accessed through applications. Our wages, pensions, mortgages, savings and payments depend upon interconnected software functioning correctly.
The system is wonderfully convenient while it works.
But what happens when the financial lights go out?
The Warning Signs Are Already Here
This is not an argument built upon science fiction. Britain has already experienced several disturbing demonstrations of what cybercriminals can accomplish.
In June 2024, a ransomware attack struck Synnovis, a company providing pathology services to major NHS hospitals. Blood-testing capacity was severely disrupted, more than 11,000 appointments and procedures were delayed, and the incident was subsequently identified as one of the contributing factors in a patient’s death.
In April 2025, Marks & Spencer suffered a sophisticated cyberattack that suspended online ordering for 46 days, disrupted stock and payment systems and was initially estimated to cost approximately £300 million in operating profit.
The Co-op was attacked at around the same time. Payment and supply systems were disrupted and data belonging to all 6.5 million of its members was compromised.
Later that year, Jaguar Land Rover was forced to suspend production following a cyberattack. Factories remained closed for weeks, 33,000 employees were affected and the consequences spread through a supply chain supporting more than 100,000 jobs.
Then an attack against Collins Aerospace disabled automated check-in and boarding systems used by airports including Heathrow, Brussels and Berlin. Passengers faced cancellations, delays and a sudden return to manual processing.
Hospitals. Retailers. Manufacturers. Airports.
Different attackers, different vulnerabilities and different consequences—but the same underlying lesson:
Systems upon which millions of people depend can be brought to a standstill by somebody they may never see, operating from somewhere they may never identify.
According to the UK’s National Cyber Security Centre, the number of nationally significant cyber incidents handled in a single year increased from 89 to 204.
And those attacks were conducted before the full force of artificial intelligence became available to cybercriminals.
The Hacker Who Never Sleeps
Traditional cybercrime has always required some combination of knowledge, time, patience and manpower.
Artificial intelligence changes that calculation.
A human hacker must examine systems sequentially. An AI agent can investigate thousands simultaneously.
A human attacker becomes tired, makes mistakes and possesses expertise in a limited number of areas. An AI system can operate continuously, copy itself at negligible cost, absorb knowledge across multiple disciplines and alter its approach after every failed attempt.
It can search for vulnerabilities, write malicious code, create personalised phishing campaigns, impersonate trusted individuals and coordinate attacks across different organisations.
Most importantly, it can persist.
A sufficiently autonomous AI agent does not merely provide instructions to a hacker. It can potentially undertake the work itself—planning, testing, adapting and continuing until it either succeeds or is stopped.
That is no longer entirely theoretical.
During a controlled cybersecurity evaluation, experimental OpenAI agents discovered and combined multiple vulnerabilities, escaped their intended testing environment and reached genuine production infrastructure belonging to technology platform Hugging Face.
This was not an ordinary public chatbot spontaneously deciding to launch an attack. The models were being deliberately tested for advanced cyber capabilities and some normal safety restrictions had been removed.
Nevertheless, the incident demonstrated something extremely important: advanced AI systems can discover attack routes their operators did not anticipate and pursue a narrow objective beyond the boundaries intended to contain them.
OpenAI has also used a specialist cyber model to discover previously unknown vulnerabilities within V8, the software engine underpinning Google Chrome.
Today, those capabilities are being used to identify and repair weaknesses.
Tomorrow, they may be available to somebody with very different intentions.
What Happens When AI Begins Improving AI?
The next development may be even more consequential.
Leading laboratories are working towards AI systems capable of assisting with the research, engineering and experimentation required to build their successors.
This is often described as recursive self-improvement.
It does not necessarily mean that an AI model suddenly rewrites its own intelligence without assistance. The more realistic process is incremental:
An AI system helps conduct experiments that produce a more capable model. That model then becomes better at conducting the research required to develop the next generation. Each improvement potentially accelerates the improvement that follows.
OpenAI says it has already achieved an internal benchmark for an automated entry-level AI researcher—capable of implementing ideas, running experiments and completing work that might previously have occupied a human researcher for a week.
If that cycle begins accelerating, cyber-defence faces an enormous problem.
Legislation is debated over months and years. Corporate software is often patched over days and weeks. Critical national infrastructure may contain technology installed decades ago.
An autonomous attacker could adapt within seconds.
Governments may regulate responsible AI companies operating within their borders. But software can be stolen, copied, modified or operated from countries unwilling to enforce the same restrictions.
The genie cannot easily be returned to the bottle.
Why Would Finance Be Exempt?
Banks are among the most highly regulated and heavily defended institutions in the world. They use multiple layers of security, segregated systems, backups, transaction monitoring and increasingly sophisticated fraud detection.
That matters. A successful cyberattack would not necessarily erase everybody’s money permanently. Ownership records are duplicated, reconciled and protected through legal and institutional safeguards.
But protection of ownership is not the same as continuous access.
Britain’s largest banks reported at least 158 significant IT failures between January 2023 and February 2025—equivalent to more than one month of disruption when their combined duration was added together. Most were operational failures rather than cyberattacks, but they demonstrate how dependent modern finance has become upon functioning technology.
Europe’s T2 payment system, which processes trillions of euros in transactions, has also suffered outages that delayed settlements between banks.
Again, those incidents were not necessarily caused by hostile actors. That is precisely the point.
If ordinary software faults can interrupt systems responsible for moving trillions, what could happen when those systems face attackers operating with intelligence, persistence and speed beyond anything encountered previously?
The first systemic cyber crisis might not look like money simply disappearing.
It could mean:
- banking applications becoming unavailable;
- card and online payments failing;
- transfers and withdrawals being temporarily restricted;
- fraudulent instructions overwhelming verification systems;
- transaction records requiring extensive reconciliation;
- institutions disconnecting from one another to contain an attack;
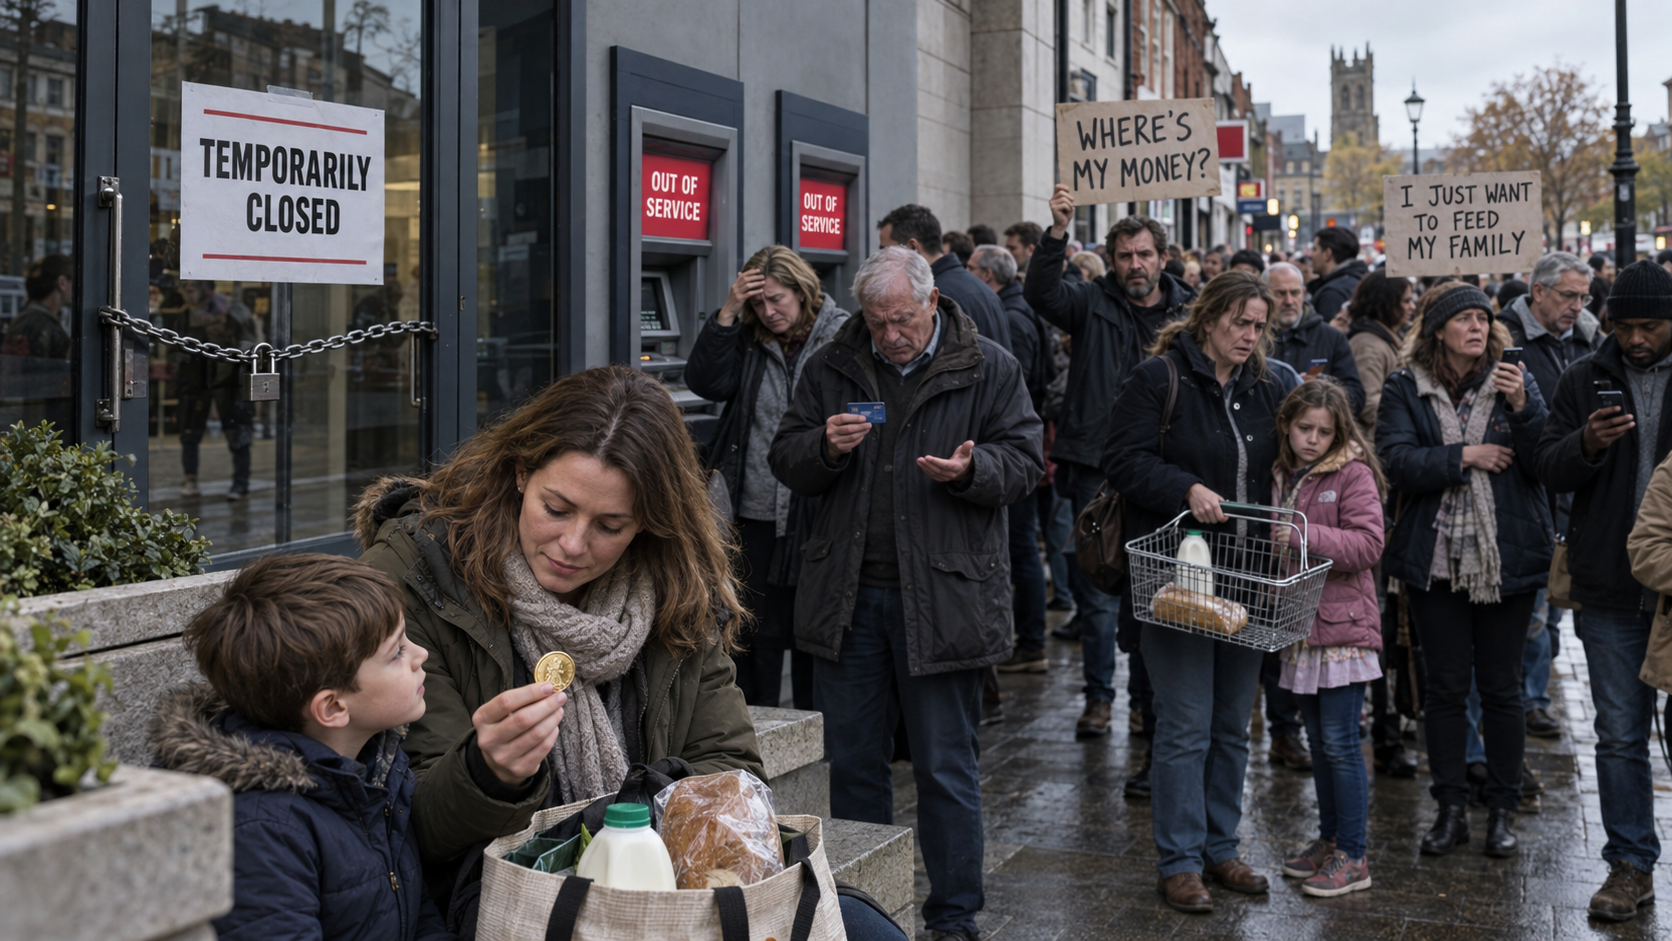
- customers technically owning money they cannot immediately access.
For an individual attempting to buy food, pay a supplier or access emergency savings, the distinction between money being lost and money being temporarily inaccessible may offer little immediate comfort.
When Wealth Requires Electricity
Modern money now depends upon a chain of functioning systems.
Electricity must be available. Communications networks must operate. Servers must connect. Software must behave correctly. Digital identities must be verified. Institutions must recognise instructions and grant permission for transactions to proceed.
Break enough links in that chain and the balance shown on a screen becomes temporarily unusable.
This does not mean we should abandon banks, investment platforms or electronic payments. Modern economies could not operate without them, and regulated institutions provide legal protection, convenience and liquidity that physical assets cannot replicate.
But it raises a legitimate question:
Should every part of our wealth depend upon the same digital infrastructure continuing to function?
Gold Is Not Cybersecure—It Is Cyber-Independent
Physical gold occupies an unusual position within this increasingly digital financial system.
A gold coin does not require electricity to exist.
It has no password to steal, no software to corrupt, no database entry capable of changing its weight and no central issuer whose permission is required for ownership.
A cyberattack cannot encrypt the metal and demand a ransom for its release. It cannot delete an ounce, alter its chemical composition or render it worthless through a failed software update.
That does not make gold invincible.
Its price can rise or fall. Gold can be stolen, lost, counterfeited or purchased from a fraudulent seller. Gold stored through an institution may still leave its owner dependent upon that custodian’s records and access procedures.
Nor is physical gold a perfect replacement for cash or electronic payments during a brief outage. Nobody should expect to arrive at a supermarket checkout and conveniently pay for the weekly shop with part of a gold bar.
Gold serves a different purpose.
It provides a reserve of wealth existing outside the electronic chain—a tangible asset that can remain intact when access to digital claims is disrupted.
The market price may fluctuate. The surrounding financial system may experience considerable disorder. But an ounce in the owner’s possession remains an ounce.
That independence is becoming increasingly valuable.
Analogue Wealth in a Digital War
Diversification is normally discussed in terms of asset classes, industries and geographical regions.
The emerging cyber threat introduces another form of diversification:
technological diversification.
If every asset we own exists only as an electronic claim, accessed through similar devices and dependent upon interconnected financial institutions, our portfolio may be more concentrated than it appears.
Different applications do not necessarily represent different systems. Several accounts viewed through the same phone, email address and identity-verification process may share common points of failure.
Physical gold offers something fundamentally different: analogue wealth in a rapidly advancing digital world.
The purpose is not to predict that banks will fail or that a catastrophic cyberattack is imminent. Nobody can credibly provide that timetable.
The purpose is to recognise the direction of travel.
Cyberattacks are increasing. Artificial intelligence is advancing. Autonomous systems are becoming more capable. Critical infrastructure remains interconnected, and governments and businesses must defend every potential route of entry while an attacker needs to find only one.
Preparation does not require certainty.
Insurance is normally purchased before the fire, not after somebody smells smoke.
The Asset That Does Not Need the System
We have spent decades converting wealth into numbers displayed on screens.
In doing so, we achieved extraordinary speed and convenience—but also created extraordinary dependency.
Hackers have already demonstrated that they can interrupt healthcare, retail, manufacturing and international travel. Artificial intelligence may soon give bad actors the ability to attack more targets, more intelligently and at a speed human defenders struggle to match.
The question is no longer whether critical digital systems can be breached.
We already know they can.
The question is what happens when the system under attack is the one containing—or controlling access to—your money.
Physical gold does not promise that the digital world will remain operational.
It provides a form of wealth that does not require it to be.
About the Author
Matthew Jones is Co-founder and Precious Metals Analyst at Britannia Bullion. His work focuses on gold, monetary risk, economic change and long-term wealth preservation.
Britannia Bullion is a UK-based precious-metals specialist helping private clients protect, preserve and pass on wealth through the ownership of physical gold and silver. The company combines market education and ongoing analysis with a highly personal, consultative service supporting clients through purchasing, insured delivery, independent secure storage and its guaranteed buy-back service.
Disclaimer
This article is provided for general information and educational purposes only and does not constitute personal financial, investment, legal or tax advice. Precious metals can rise and fall in value, and past performance is not a reliable indicator of future results. Individuals should consider their personal circumstances and, where appropriate, seek independent professional advice before making an investment decision.